How we process data
On this page 10 sections
This page is published by WhealBit of St Ives, Cornwall (“Splash”, “we”). It sets out, in the format of a data processing agreement, how we and our sub-processors process personal data to run Splash. It forms part of our Privacy Policy and should be read with the Sub-processors list and our security page.
Why there is no DPA to sign
WhealBit’s business products (such as WagePilot) process staff data on behalf of employers, so they offer an Article 28 Data Processing Agreement for those customers to sign. Splash is different. It is a free consumer app: you use it for yourself, and we are the controller of the limited personal data we hold. There is no business customer, so there is no controller–processor contract between you and us. Instead, this page records the same information a DPA would, so you can see exactly how processing works, and our own contracts with our sub-processors meet Article 28.
1. Roles
- WhealBit is the controller for account data, encrypted backups, partner-share records and notification records.
- Supabase and Vercel process data as our processors (our “sub-processors”), on our written instructions only.
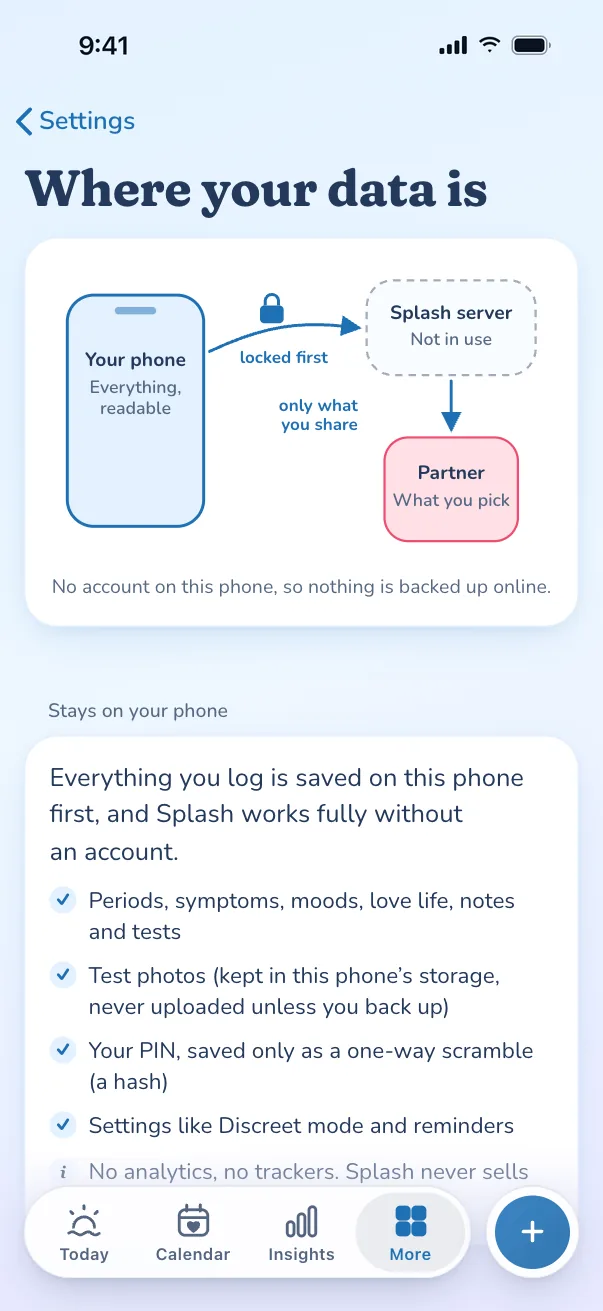
- You hold the keys. Your health data is encrypted on your device, so no one in this chain can read it.
- Browser push services, Google (emoji images) and Hugging Face (optional voice model) act as independent controllers for the limited technical data they receive.
Annex 1: Details of processing
| Subject matter | Providing optional accounts, encrypted backup and sync, partner sharing and push notifications for the Splash app |
|---|---|
| Duration | For as long as you keep an account; until deletion as set out in section 7 |
| Nature of processing | Storage, retrieval, transmission and deletion. We do not decrypt, analyse, profile or combine health data, and cannot |
| Purpose | Back up and sync your data between your devices; pass encrypted snapshots to partners you choose; deliver notifications you turn on |
| Data subjects | Splash account holders; partners who open a share or reply; people who contact us |
| Personal data | Email address, password hash, session records, optional display name, sync metadata, share categories and dates, push addresses, notification text and times, technical request data |
| Special category data | Cycle, sexual and reproductive health data, only as end-to-end-encrypted ciphertext that neither we nor our sub-processors can read. Lawful basis: your explicit consent (Art. 9(2)(a)) |
| Storage location | Supabase, Paris, France (EU, eu-west-3) |
Annex 2: Technical and organisational measures
- End-to-end encryption: AES-GCM with 256-bit keys, with a fresh random 12-byte IV for every encryption. Data is encrypted on your device before upload.
- Keys stay with you: a random vault key, wrapped with a key derived from your recovery code (PBKDF2-SHA256, 310,000 iterations, random 16-byte salt). We never receive the recovery code or an unwrapped key.
- Partner shares: separate per-share keys carried only in your QR code or link; we store a SHA-256 of the share key to check access, never the key.
- Access control: Postgres row-level security on every table, so each account can only reach its own rows; server-side functions for the few cross-account actions.
- In transit: TLS for every connection; strict content security policy on the app and website.
- Minimisation: no analytics or tracking SDKs, no advertising identifiers, short retention for replies (3 days) and sent notifications (14 days).
- People: access to production systems is limited to the people who run Splash, using strong authentication.
3. Sub-processing
We use only the sub-processors on the Sub-processors list, each under a written contract with data protection obligations meeting Article 28(3) of the UK GDPR. We remain responsible for them. We will update the list before adding or replacing a sub-processor that handles account or backup data, and tell account holders in the app.
4. Location and international transfers
Account data and encrypted backups are stored in the EU, in Paris, France (eu-west-3). UK-to-EEA transfers are covered by the UK’s adequacy regulations for the EEA. Where a provider processes data in, or accesses it from, a country without UK adequacy (for example Vercel’s global edge network, or US-based support access), we rely on an Article 46 safeguard such as the ICO International Data Transfer Addendum to the EU Standard Contractual Clauses, or the UK Extension to the EU-US Data Privacy Framework where the provider is certified.
5. Personal data breaches
If we become aware of a personal data breach, we will contain it, assess the risk, and report it to the ICO within 72 hours where required. If it is likely to result in a high risk to you, we will tell you without undue delay. Because health data is stored only as ciphertext, a breach of our database would not expose it in readable form.
6. Helping you with your rights
Most rights are self-serve in the app (export, edit, delete, turn sync or sharing off, delete account). For anything else, email hello@splash.care and we will respond within one month.
7. Deletion and return
You can export your data from the app at any time. Deleting your account removes your account, encrypted backups, shares, push subscriptions and scheduled notifications from our database straight away. Provider backups age out on their normal cycle.
8. Records and review
We keep a record of processing activities and review this schedule, our security measures and our sub-processors when the app changes and at least once a year.
Related legal documents
Questions about any of these? Email hello@splash.care.
Without an account, none of this reaches us.
Your cycle stays on your phone by default. Free, no data sales.